Tag: AI security
Red Teaming for Privacy: Testing LLMs for Data Leakage
Discover how red teaming protects LLMs from data leakage. Learn methodologies, tools like NVIDIA garak, and regulatory impacts to secure your AI deployments.
- Nov 10, 2026
- Collin Pace
- 4
- Permalink
Prompt Injection in LLMs: Attacks, Defenses & Best Practices
Discover how prompt injection threatens LLMs, why it differs from SQL injection, and effective defense strategies like context partitioning and output validation.
- Aug 31, 2026
- Collin Pace
- 9
- Permalink
Input Validation for LLM Applications: How to Sanitize Natural Language Inputs to Prevent Prompt Injection Attacks
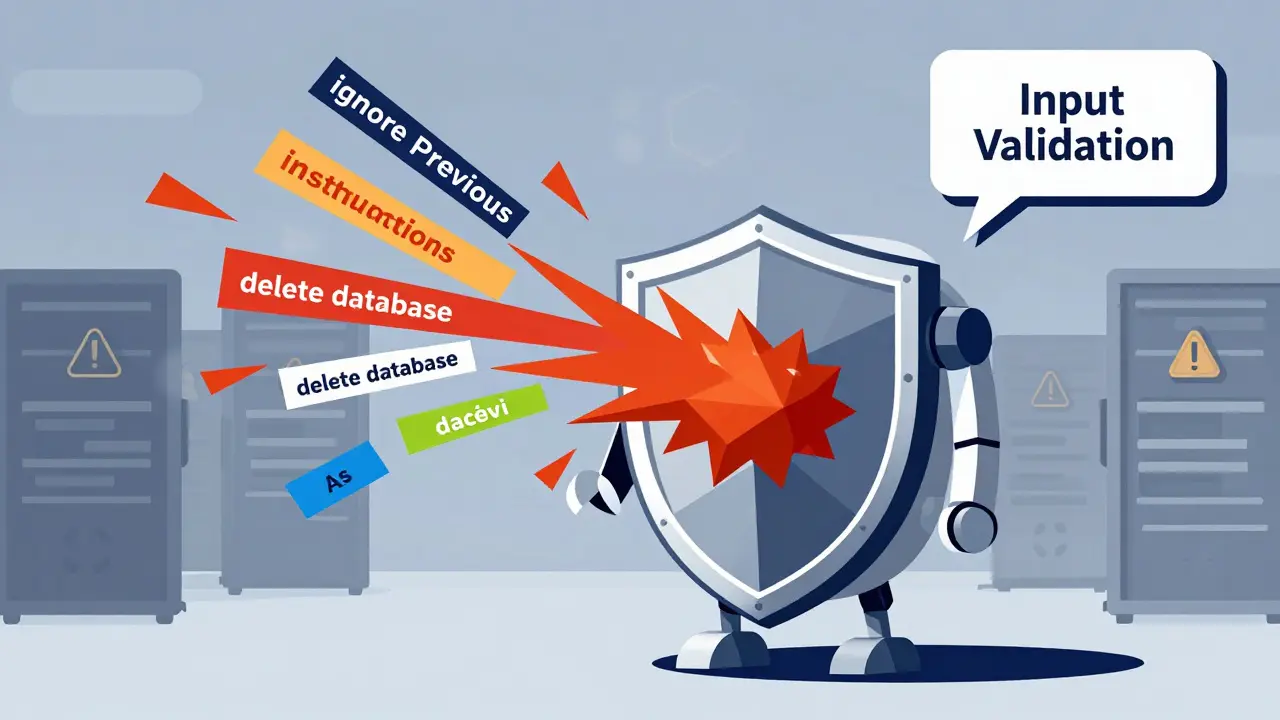
Learn how to prevent prompt injection attacks in LLM applications by implementing layered input validation and sanitization techniques. Essential security practices for chatbots, agents, and AI tools handling user input.
- Jan 2, 2026
- Collin Pace
- 9
- Permalink